Mahmoud left his workstation unlocked during a short break. While he was away, an insider accessed the machine and performed unauthorized activity. When he...
Digital ForensicsMemory ForensicsVolatilityInsider ThreatIncident ResponseEYCC CTF 2026beginner-friendly
Cant pay for Photoshop? We got you. we give you photoshop FOR FREE. if you want it download the file now and run it, it will do everything else dont worry.
Uncovering a high-severity authentication logic and token validation flaw in an application portal leading to full account takeover and a top bounty payout.
How a path traversal and broken access control flaw allowed escalating privileges from a low-privileged account to Admin across 150 administrative endpoints.
Mahmoud was chatting with a colleague and asked them to send the required work files. With good intentions, he opened the received file, but shortly after, he...
Digital ForensicsDisk ForensicsPhishingLOLBinsPersistenceMITRE ATT&CKEYCC CTF 2026beginner-friendly
Our friend Ragab Ganbar is tired from warming the bench of unemployeds' groupجروب العواطلية, at a moment of desperation he decided to start his own RaaS.
After getting caught twice, Ganbar found a tutorial that uses a unique language and he decided to try it on his next victim ByeSword company. Can you catch him...
Solving the OSINT challenge from CTF@CIT 2026 — cracking a password-protected PDF, performing username enumeration, and investigating target profiles across...
If you want to download the challenge and try to solve it by yourself this is the link for the challenge: Analysis First I make checksec to check the...
Solving 'Season' web challenge in CyCTF Luxor CTF 2026 Finals, the challenge involves bypassing weak XXE validation and uploading a shell in php for rce
it is 0x2face with another writeup , this one will be about the linux jails , mic challenges , crypto challenges i created in CAT CTF entry Level CTF 26 , lets...
it’s 0x2face with another cool osint writeup , but this time as a challenge Author , i am happy to contribute to CAT Reloaded entry level CTF AS An Author this...
Solving the Android track of CyCTF Luxor — extracting a token from exported SharedPreferences, recovering an AES-ECB key from the signing cert, and forging a...
Analysis First I made checksec to check the mitigations on the binary checksec ./apppatched Arch: amd64-64-little RELRO: Full RELRO Stack: No canary found NX:...
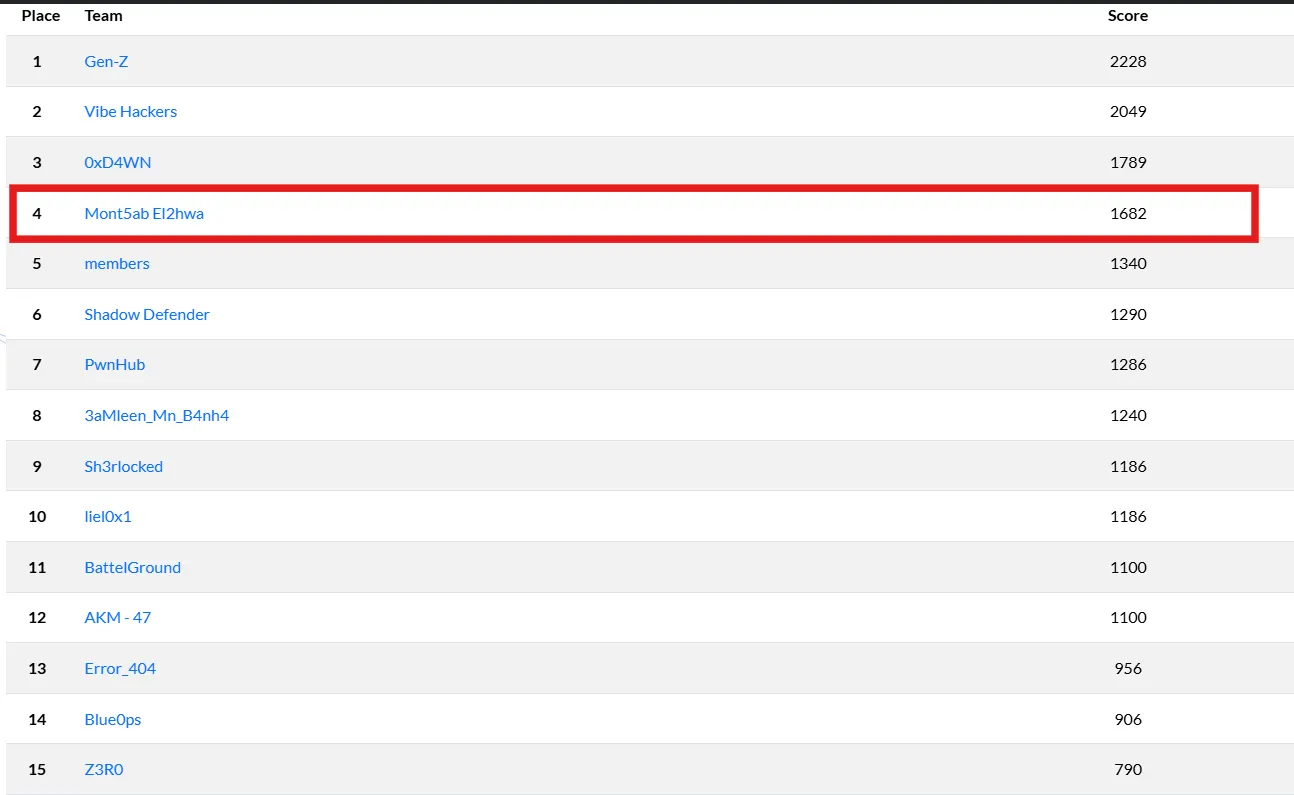
hi there hackers, it’s 0x2face with another Osint ctf writeup , this time it’s from 0xfun ctf , i am proud to share that our team M0nt5ab El2hwa secured 9th...
An OSINT investigation starting from a single ransom image left on a Node.js developer machine. Trace the attacker across all platforms to uncover an attack...
1- Challenge Idea The Program TickTock.exe does the following: Builds an array of numbers from 1 to 105 as bytes Randomly selects 32 bytes from it → this...
Solving “Auditor” challenge from FahemSec, where SSRF was achieved through Apache Content-Type/header injection to reach an internal Flask service and retrieve...
hi there hackers, it 0x2face with another osint write-up , this time it is 0xl4ugh CTF V5 , the ctf was challenging , amazing and i had great experience from...
hi there, back after a while , but this time as an author not a player , i am happy to be an author for the GDG Benha core team ctf competition , this...
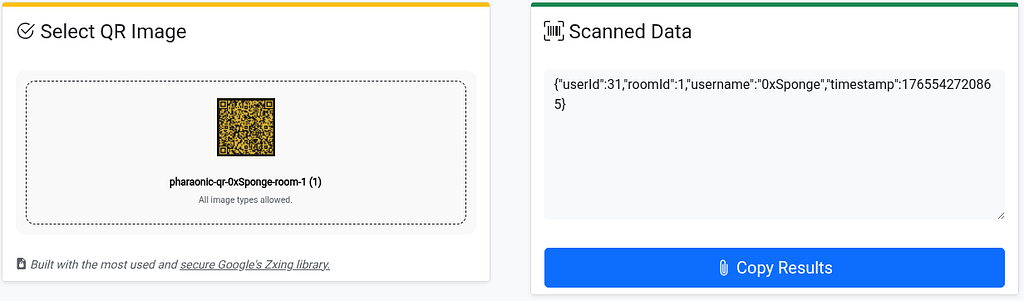
Chaining a path-traversal in an admin bot's QR-scan handler with an over-trusted promote endpoint to escalate a normal user to admin and reach the flag room.
Solving 'BugZzzz' challenge from Fahemsec, where you can only register with @fahmsec.ctf but the problem you are provided with mail @example.com so you can...
Here we will be solving 3/4 DFIR for HTB CTF it was a solo one and I ranked 74 not the best but I focused more on Forensics so lets start Manual very easy...
An advanced DFIR analysis bridging disk and memory forensics to uncover hidden Zoom artifacts. This walkthrough details the step-by-step process of VSS...
Solving three web challenges from IEEE Mansoura CTF Qualifications 2025, featuring exploitation techniques such as XSS, CSP bypass, admin bot abuse, and Bottle...
Solving the web challenge 'cat flag.png' from Connectors CTF 2025 — exploiting command injection to exfiltrate a hidden flag image via hex-encoded binary data...
Solving all web challenges from IEEE CTF Qualifications 2025, covering XSS CSP bypass, RCE via Pickle deserialization, XSS through prototype pollution, blind...
Bypassing a broken XSS filter in a context using JavaScript hoisting to defeat a ReferenceError guard, then exfiltrating the admin bot's cookies via Burp...
hi there , this is me abdelrahman ahmed aka 0x2face , and i play osint / steganagoraphy / web challenges in ctfs , but in this ctf my main focus was osint...
Hello, I’m Abdelrahman Ahmed aka 2FACE, and i participated for the first time with my team “Liel0x1" in the ASCWG 2025 and i am proud to share that we made it...
Solving three web challenges from ASC Cyber WarGames 2025 Qualifications, covering exploitation techniques such as IDOR, JWT forgery, SQL injection, race...
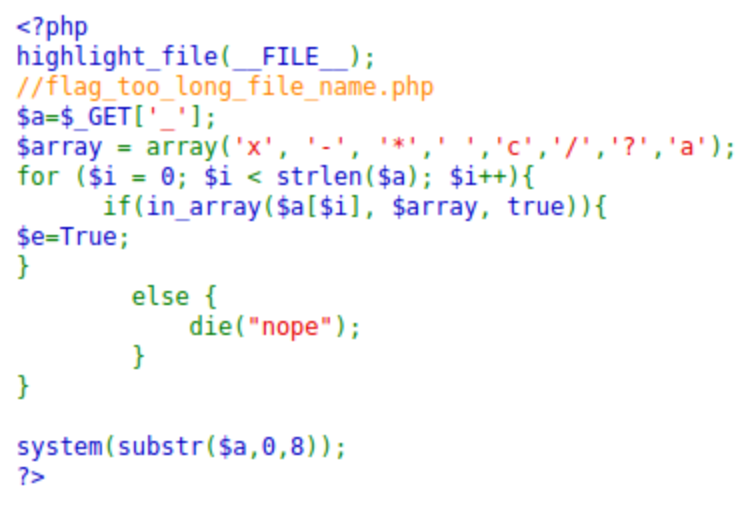
Write-ups for web and reverse engineering challenges from ICMTC CTF 2025 Finals, covering a PHP command execution wildcard bypass, decompilation of compiled...
Challenge Description: In an era fraught with cyber threats, Talion “Byte Doctor” Reyes, a former digital forensics examiner for an international crime lab,...
First challenge: Map Volnaya’s Industrial Influence Network What should we do here is to Identify the shell company used by Volnaya Corporation SVIR to procure...
All OSINT Challenges → Ch1: The Poisoned Scroll Challenge Description: Nyla, Eldoria’s master information seeker, investigates a series of magical attacks on...