Web Writeups
Solutions, exploit walkthroughs, and challenge analysis in Web.
WebWhiteboxWeb ExploitationBusiness Logic FlawDatabase ConstraintsPath TraversalEYCC CTF 2026beginner-friendlywhitebox
@Agn4by // EYCC CTF 2026
Read →
WebCTF Challenge
Mall Albostan
Mall Albostan, Downtown Cairo's go-to spot for laptops, GPUs, and everything in between...
WebWhiteboxSQL InjectionJWT ForgeryFile Upload BypassXXE InjectionRCEEYCC CTF 2026beginner-friendlywhitebox
@00xcanelo // EYCC CTF 2026
Read →
Web
No JS | AlpacaHack
Solving 'No JS' web challenge in AlpacaHack, the challenge involves client-side attack
Client Side
@00xcanelo // AlpacaHack
Read →
Web
CyCTF Luxor 2026 | web Finals
Solving 'Season' web challenge in CyCTF Luxor CTF 2026 Finals, the challenge involves bypassing weak XXE validation and uploading a shell in php for rce
XXEPHP file uploadRCE
@00xcanelo // CyCTF
Read →
Web
CAT CTF 26 — Entry Level
Solving all web challenges for CAT CTF 26 — Entry Level, covering bugs like LFI, SSTI, DOMPurify bypass, lfi2rce, and SSRF via EC2 metadata service.
LFISSTIAPIDom purify bypass
@00xcanelo // CAT Reloaded CTF
Read →
Web
CyCTF Luxor web Qualifications
Solving all web challenges in CyCTF Luxor Qualifications, covering a mix of Next.js, race condition, and CRLF issues.
nextjsrace conditionCRLF
@00xcanelo // CyCTF
Read →
Web
0xL4ugh CTF — Smol Web
Smol Web بسم الله الرحمن الرحيم Hello Hackers, I’m !/bin/bash , back again with some web challenges from 0xl4ugh ctf 2025 edition.
@0xheg3zy // 0xL4ugh CTF
Read →
Web
SSRF via Content-Type in Apache — Auditor
Solving “Auditor” challenge from FahemSec, where SSRF was achieved through Apache Content-Type/header injection to reach an internal Flask service and retrieve...
Apacheheader injection
@Agn4by // FahemSec
Read →
Web
pdf.exe | 0xL4ugh v5 CTF
Solving 'pdf.exe' Insane web from 0xl4ugh v5 CTF, featuring two 0days: a Next.js SSRF and a PDFKit file-read vulnerability.
0dayNextjspdfkit
@00xcanelo // 0xL4ugh CTF
Read →
Web
Night at the Museum
Chaining a path-traversal in an admin bot's QR-scan handler with an over-trusted promote endpoint to escalate a normal user to admin and reach the flag room.
path-traversalprivilege-escalationbroken-access-controlapi
@0xsponge // FahemSec
Read →
Web
BugZzzz | Fahemsec
Solving 'BugZzzz' challenge from Fahemsec, where you can only register with @fahmsec.ctf but the problem you are provided with mail @example.com so you can...
ResearchAccess control bypass
@00xcanelo // FahemSec
Read →
Web
OhMyPP Web challenge | PWNSEC CTF 2025
Solving a web challenge exploiting prototype pollution to achieve the intended goal.
Prototype pollution
@00xcanelo // PWNSEC CTF
Read →
Web
IEEE Mansoura CTF Qualifications 2025
Solving three web challenges from IEEE Mansoura CTF Qualifications 2025, featuring exploitation techniques such as XSS, CSP bypass, admin bot abuse, and Bottle...
CSP bypassXSSBottle deserialization/RCE
@Agn4by // IEEE Mansoura 2025
Read →
Web
cat flag.png
Solving the web challenge 'cat flag.png' from Connectors CTF 2025 — exploiting command injection to exfiltrate a hidden flag image via hex-encoded binary data...
Command InjectionDNS Exfiltration
@babayaga0x01 // Connectors CTF
Read →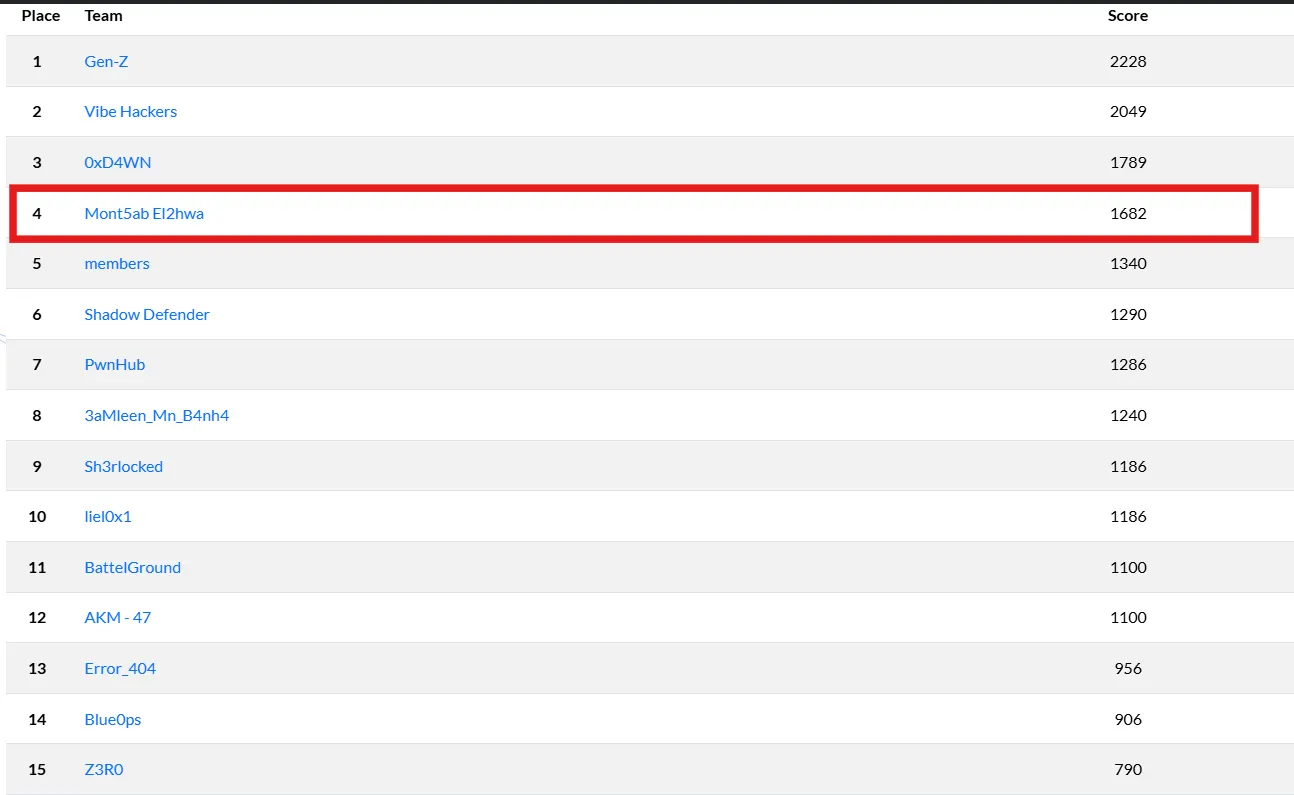
Web
All Web & MISC Challenges IEEE CTF 2025
Solving all web challenges from IEEE CTF Qualifications 2025, covering XSS CSP bypass, RCE via Pickle deserialization, XSS through prototype pollution, blind...
blind sqliXSSCSP bypassRCEdeserializationstegno
@00xcanelo // IEEE Mansoura CTF
Read →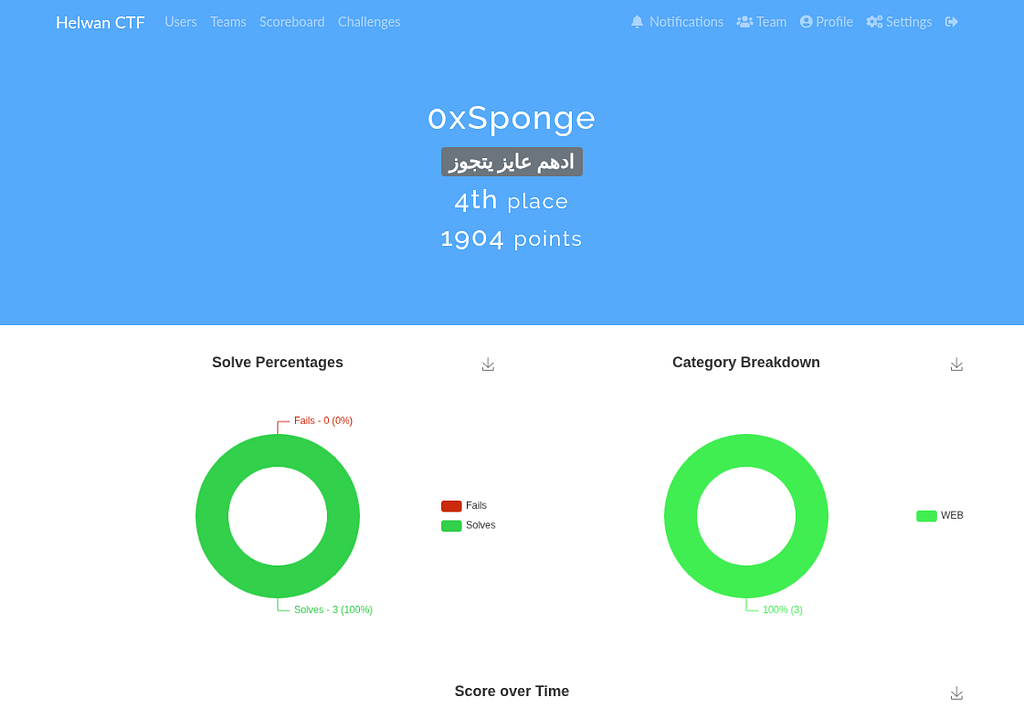
Web
[Tob] WEB challenge
Bypassing a broken XSS filter in a context using JavaScript hoisting to defeat a ReferenceError guard, then exfiltrating the admin bot's cookies via Burp...
xssjavascript-hoistingcookie-exfiltrationbot
@0xsponge // Helwan CTF
Read →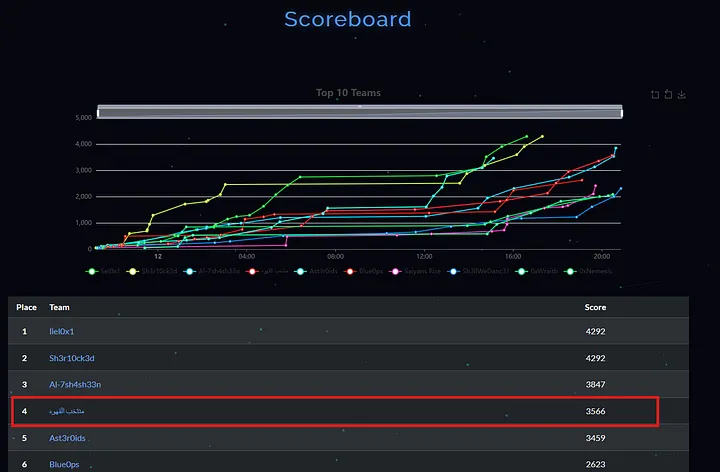
Web
All Web Challenges Connectors CTF| منتخب القهوة
Solving all web challenges from Connectors CTF Qualifications, which includes bugs like Logical bugs, XSS via PDF,etc...
Logical BugsRCEFlask
@00xcanelo // Connectors CTF 2025
Read →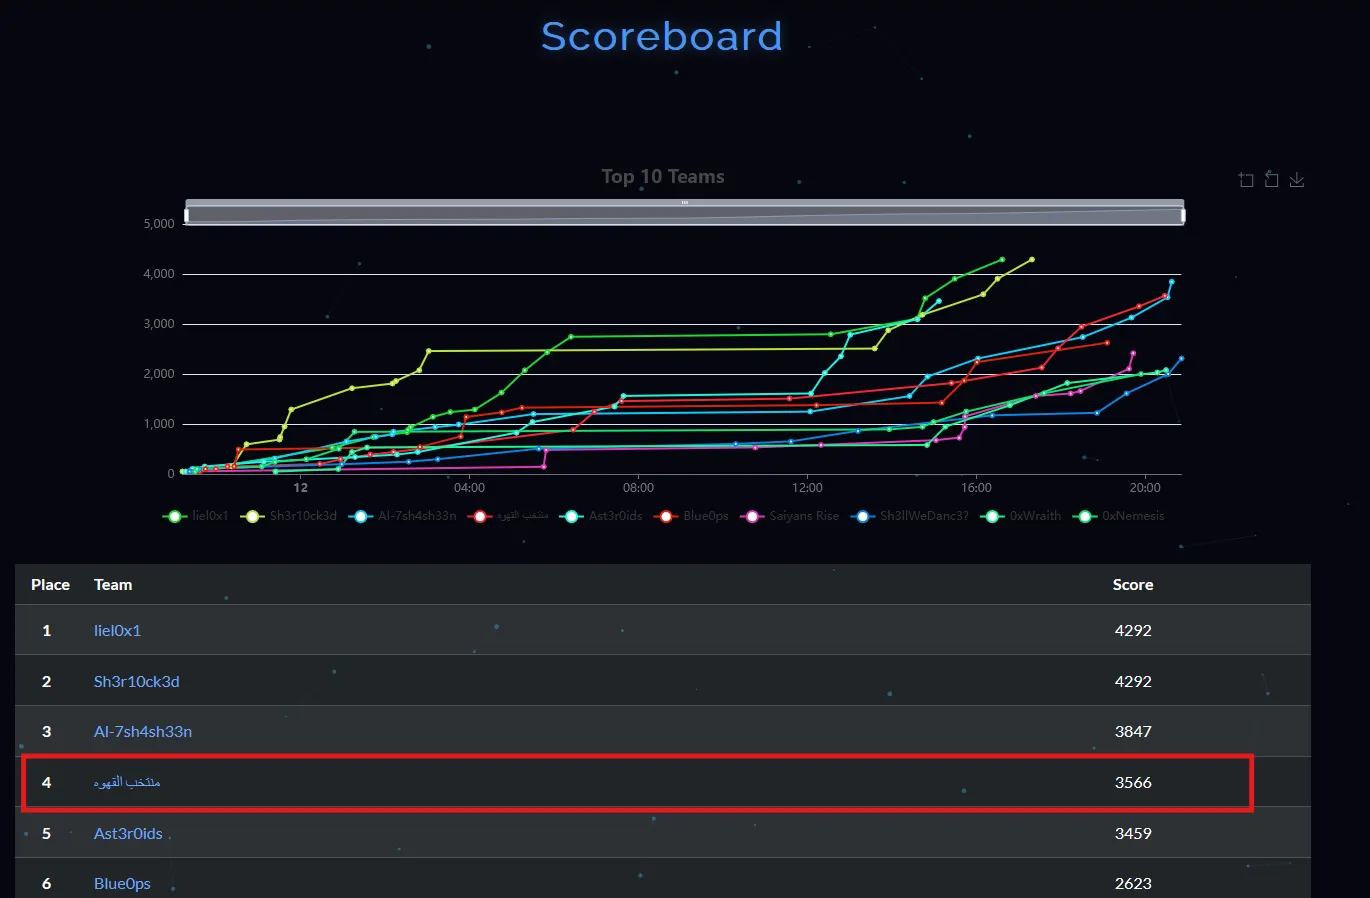
Web
All Web Challenges Connectors CTF | منتخب القهوة
Solving all web challenges from Connectors CTF Qualifications, which includes bugs like logical bugs, XSS via PDF, etc.
Logical BugsRCEFlask
@00xcanelo // Connectors CTF
Read →
Web
Stylish-Boss
Exploiting CSS injection and command injection to bypass CSP and steal admin API keys, leading to full system compromise in a web challenge.
Command InjectionCSS Injection
@babayaga0x01 // CAT Reloaded CTF
Read →
Web
ASC Cyber WarGames Qualifications 2025
Solving three web challenges from ASC Cyber WarGames 2025 Qualifications, covering exploitation techniques such as IDOR, JWT forgery, SQL injection, race...
sql-injectionPhar Deserializationjwtrace condition
@Agn4by // ASC Cyber WarGames
Read →
ReverseWeb
ICMTC CTF 2025 Finals
Write-ups for web and reverse engineering challenges from ICMTC CTF 2025 Finals, covering a PHP command execution wildcard bypass, decompilation of compiled...
icmtc-ctfctf
@0xheg3zy // ICMTC CTF
Read →
Web
ICMTC CTF 2025 - Qualifications
Write-ups for web, pwn, and reverse engineering challenges from ICMTC CTF 2025 Qualifications, covering Flask session cookie forgery, XSS cookie theft, Pickle...
path-traversalsession-forgeryxssdeserializationrcegraphqlbuffer-overflowbinary-exploitationreverse-engineeringctf
@0xheg3zy // ICMTC CTF
Read →